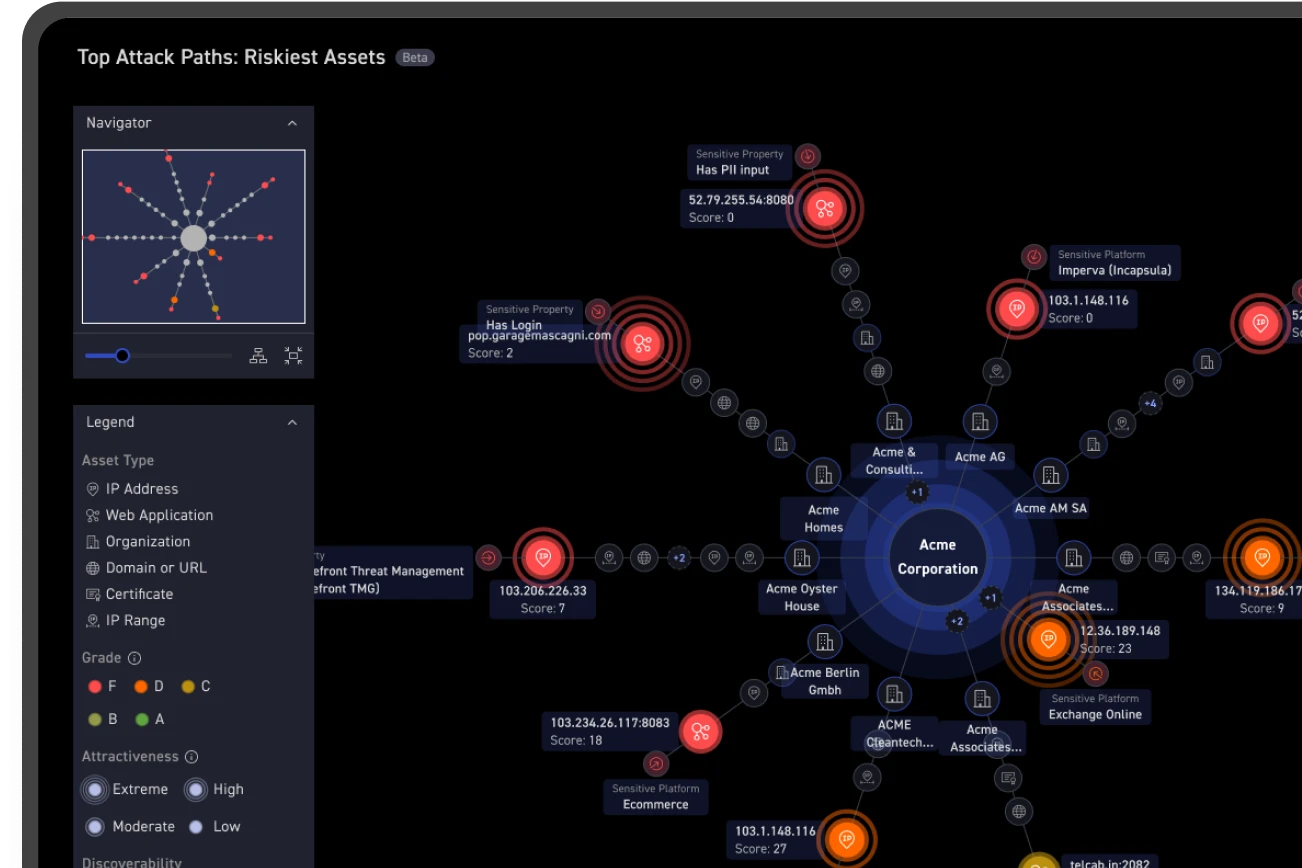
Today we are happy to announce the beta release of the CyCognito MCP server, which makes your external attack surface data consumable by any AI client that speaks the Model Context Protocol, including Claude, Cursor, and ChatGPT.
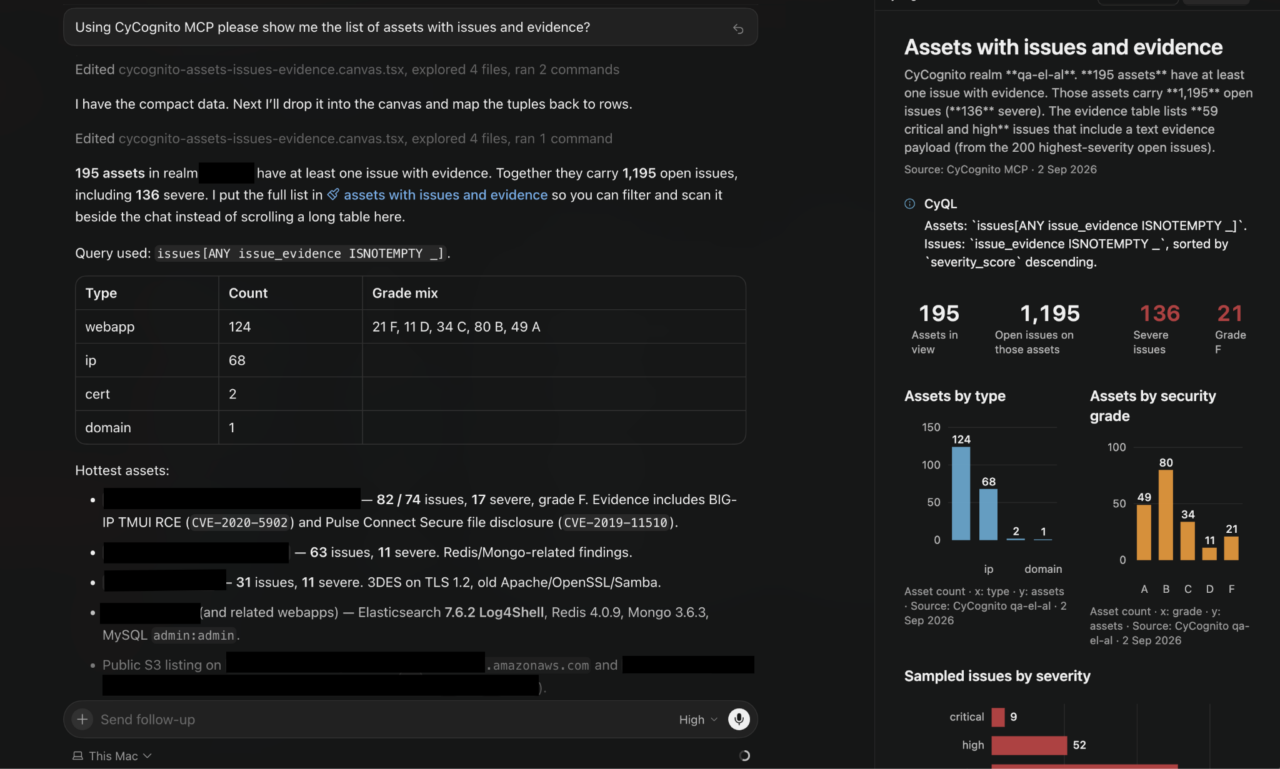
The server runs on CyQL, the proprietary query language behind advanced search in our platform. CyQL is designed to ask precise questions about an attack surface, using operators suited to each type of asset, issue, and relationship.
At the time of release, the server capabilities include:
- Realm-wide search across all assets and issues
- Detailed access to all asset and issue records, including related evidence
- Access to archived issues for retrospective analysis
- Ability to translate free text to CyQL
Together, these offer quick, easy, and flexible access to a robust pool of exposure data spanning over 150 properties, covering technical and business context as well as relevant threat intelligence.
The server is read-only, every request going through it is logged. Access is granted solely on the basis of the privileges you already have in the platform, which cascade into the MCP server, so each user sees exactly what they would see in the platform and nothing more.
The MCP server is available now, in both our EU and US environments. Contact your customer success manager to enable it for your account.
Why an MCP server for exposure management
I know this one pretty much answers itself. Still, at the risk of stating the obvious, the way security teams work is changing. When investigating an issue or putting a report together, teams now often chain together AI agents, or lean on other AI capabilities. For all of those, MCP data access turns into an obvious requirement rather than a nice-to-have.
The less obvious part is specific to external attack surface data. Analyzing exposure information is most useful when you can connect the dots to internal data (e.g., via a CMDB system). An AI client that can cross-reference several tools at once gives you a deeper and more contextual view, and MCP is the bridge that enables it.
Taking things a step further, the data provided via MCP can also connect to other systems, including ITSM and ticketing, for ownership information and remediation acceleration.
Practical use cases
To help you get started, here are some ways in which we already see teams thinking about utilizing our MCP server. These offer a good starting point to build upon for more advanced use cases.
Morning triage
Start the day by asking what changed on your external surface in the last 24 hours. The AI client returns the issues that opened, ranked by priority, enabling you to pick the ones that matter most, and offering a full record with the evidence attached. From there you can hand the owning team something they can act on.
Attribution questions
Another common one is why an asset was attributed to a subsidiary, and here you get the reasoning behind the decision. Most security tools can only describe infrastructure you already told them about. Attribution works the other way around, because the job is establishing that an unfamiliar domain belongs to a company you acquired three years ago and never documented.
Finding unmanaged assets
Because the AI client can use several tools in one session, you can ask it to compare the internet-facing assets we discovered against your CMDB and list the ones that appear in ours and not in yours.
What’s next
Two things are already on the roadmap. The first is broader coverage of the platform’s data model, including organizational data and other useful datapoints
The second is write access, which we are taking slowly on purpose: letting an agent change state in a security platform needs scoping, approval, and an audit worked out first.
Stay tuned.